CLEAR Framework v0.6
Cognitive Load and Escalation Assessment for Regulated environments
Every major regulatory framework governing technology risk and incident response mandates human oversight of systems. None of them govern the cognitive readiness of the teams executing that oversight. The CLEAR Framework addresses that governance gap across MAS FSM-N05, NIST SP 800-61r3, and MAS TRM 2021, selected because these are the instruments where the gap is most consequential for regulated financial services in Singapore.
v0.6, August 2026. In active peer review. Not for public distribution.
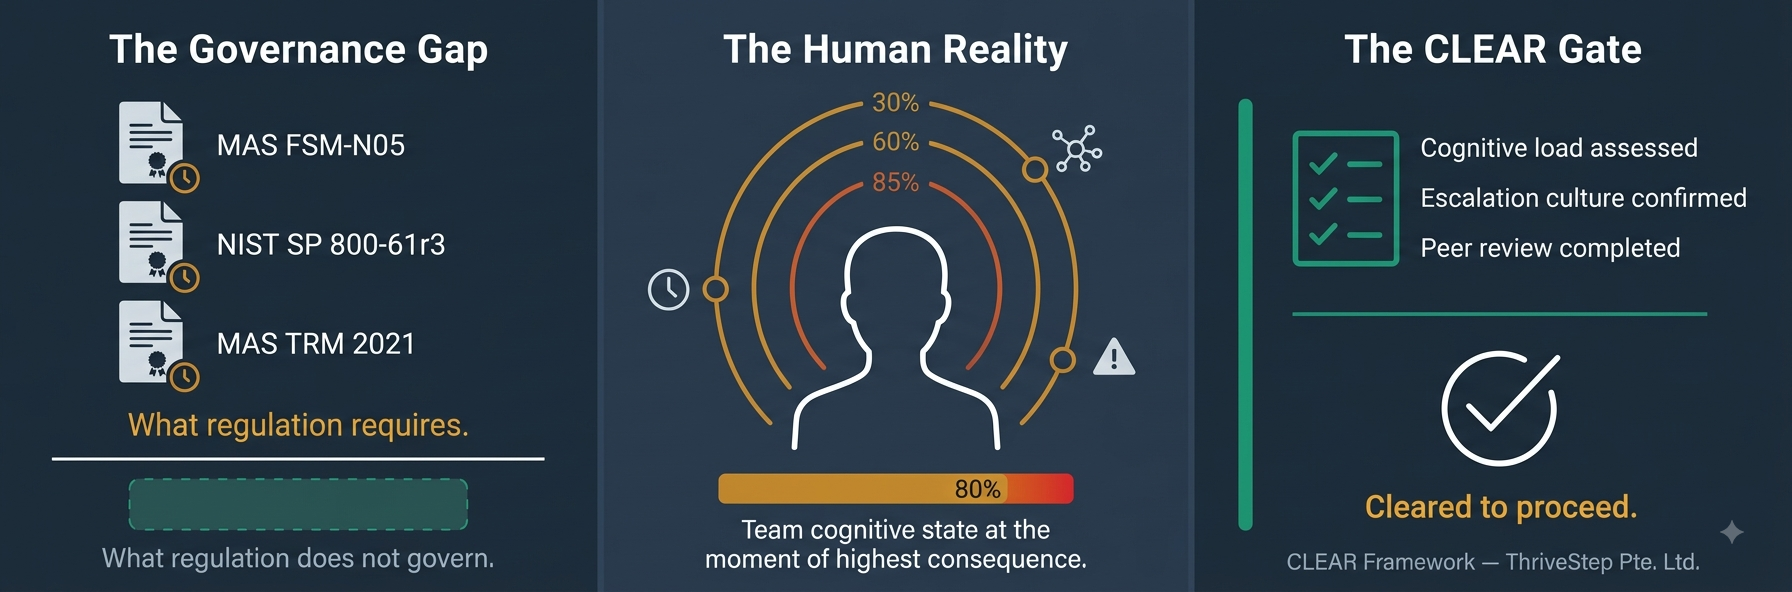
The CLEAR Framework: governance gap, human reality, and the gate response. ThriveStep Pte. Ltd.
What regulation requires.
What regulation does not govern.
Three instruments govern technology risk and incident response in regulated financial services organisations in Singapore and globally. Each mandates human oversight at critical decision points. None specifies whether the humans at those decision points are in a cognitive condition to exercise that oversight soundly.
Requires Singapore financial institutions to notify MAS within one hour of discovering a relevant incident. That notification is made by a senior management team, convened under time pressure, on incomplete information, while simultaneously managing containment, communications, and legal. The obligation is specified. The team's readiness to execute it is not.
Notes that adverse event volumes are high and that automated filtering reduces datasets to a subset suitable for human review. The human review layer is explicitly identified as a load concentration point where analytical capacity and decision quality are most exposed. The framework identifies this load. It does not govern it.
Section 3.5 expects that financial institutions ensure personnel have the requisite competence to perform IT functions and manage technology risks. Competence is expected. The conditions under which that competence can actually be exercised: under sustained operational load, during extended incident response, or in programme recovery: are not specified.
The gap is not in what the frameworks say. It is in what they presuppose but do not specify. MAS TRM expects competence. It assumes the conditions for exercising that competence exist. A team operating under sustained cognitive load, at hour three of an active incident, is not operating at competence regardless of their training or credentials. CLEAR addresses the governance layer that regulatory frameworks mandate but do not instantiate.
Three domains.
Fifteen assessment gates.
CLEAR maps structured cognitive readiness assessment gates to existing compliance checkpoints in MAS TRM, NIST SP 800-61r3, and ISO 27035. It is designed to overlay on governance structures organisations already have, not be built from scratch. Gate-level procedures and assessment thresholds are documented in the full framework.
Maps to the full incident lifecycle as defined in NIST SP 800-61r3 CSF 2.0 and MAS Notice FSM-N05. Gates are identified by domain prefix and sequence number: IR-1 through IR-5, TRM-1 through TRM-5, and PD-1 through PD-5. Covers team baseline at mobilisation, alert triage readiness, the FSM-N05 notification decision, extended operations, and post-incident review. Each gate specifies the instrument, the administration trigger, and the escalation threshold.
Maps to MAS TRM 2021 best practice sections covering board and senior management oversight, cyber assessment team readiness, SOC cognitive load monitoring, IT project escalation culture, and security training effectiveness. Distinguishes between binding Notices and best practice Guidelines throughout. Uses "expects" for MAS TRM, "requires" for FSM-N05.
Maps to MAS TRM 2021 Section 5 and PMI Pulse of the Profession 2025. Covers team mobilisation psychological safety, discovery phase cognitive load, gate review panel readiness, recovery under compounded load, and lessons learned review culture. Gate PD-4 specifically addresses the most frequently encountered pattern in distressed programme work.
Three validated instruments.
Under five minutes each.
Every assessment instrument in the CLEAR Framework is independently validated in the peer-reviewed literature. None requires specialist administration. All produce team-level aggregate scores: no individual attribution, no performance record. The gate procedures specify precisely when each instrument is triggered, how findings are documented, and what escalation thresholds apply.
Six-dimension subjective workload assessment administered at the point of highest operational consequence. Produces a weighted composite score across mental demand, physical demand, temporal demand, performance, effort, and frustration. Used across aviation, military, healthcare, and cybersecurity environments.
Hart and Staveland (1988). Under five minutes to administer and score. Deployed at IR-1, IR-3, IR-4, TRM-2, TRM-3, PD-2, PD-4.
Periodic team-level burnout baseline across three dimensions: exhaustion, cynicism, and professional efficacy. Administered as an aggregate survey with no individual attribution. Findings inform resourcing decisions, rotation planning, and board-level workforce risk reporting: never individual performance records.
Maslach, Jackson, Leiter. Validated across regulated professional environments. Deployed at IR-1, TRM-2, PD-4. Requires HR and legal sign-off before first deployment.
Seven-item validated instrument measuring team psychological safety: the degree to which team members feel safe to surface risk signals, raise concerns, and escalate without fear of reprisal. Predicts early risk escalation behaviour and error-catching capacity. Received Outstanding Publication in Organisational Behaviour award from the Academy of Management.
Edmondson (1999), Administrative Science Quarterly. doi:10.2307/2666999. Deployed at IR-5, TRM-4, PD-1, PD-3, PD-5.
A governance overlay.
Not a replacement.
CLEAR sits at the layer that COBIT, ISO 27001, NIST, and MAS TRM assume but do not specify. It does not require new governance infrastructure, new headcount, or specialist platforms. Understanding its precise scope prevents the most common implementation failure modes.
Post-peer-review edition.
v0.7 in preparation.
CLEAR v0.6 has been structurally revised following substantive peer review. It is grounded in peer-reviewed research and primary regulatory sources. A public overview document is available below. The full framework is shared on request after a brief conversation.
Rigorous before it is wide.
CLEAR v0.6 incorporates twelve structural revisions following peer review: regulatory instrument selection rationale, Visual Summary, Framework Design section, outcome evidence by domain, checkpoint map application notes, Glossary of Abbreviations, and Conclusion. The full framework is shared on request. An NDA is required before distribution. A public overview is available on this page. Substantive observations from peer review have been incorporated into v0.6.
The gate-level procedures, scoring thresholds, implementation methodology, and assessment instrument guidance are not published on this page. The full framework document is shared via direct message after a brief conversation confirming context.
Request the CLEAR Framework
Public Overview Document
A framework overview covering the governance gap argument, three-domain architecture, assessment instruments, design principles, and implementation journey. Does not contain gate-level procedures or assessment thresholds.
Read the CLEAR Framework OverviewIf you are working through this governance gap in your organisation: whether in incident response, technology risk oversight, or regulated programme delivery: connect directly via LinkedIn or email. The conversation is exploratory. There is no commitment implied on either side.
Framework shared via direct message. Not for public distribution or onward sharing without permission of ThriveStep Pte. Ltd.